DFSA and Cambridge initiative publish agentic AI cyber resilience paper
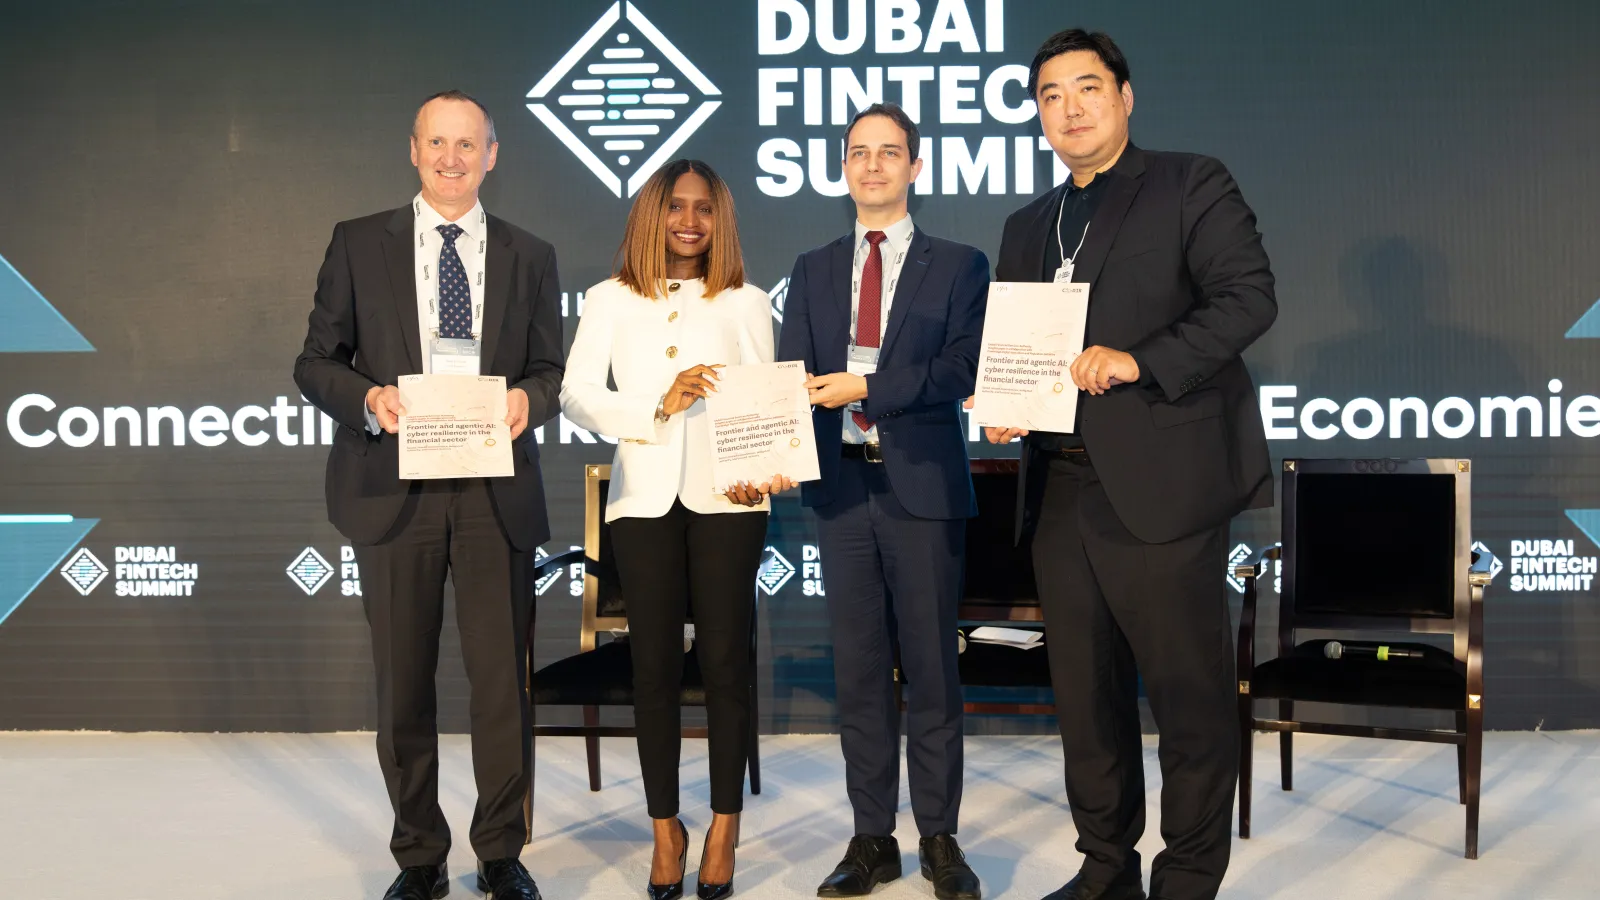
The Dubai Financial Services Authority (DFSA) and the Cambridge Digital Innovation and Regulation Initiative (C:\>DIR), an initiative of Financial Innovation for Impact, have jointly published a discussion paper examining how frontier and agentic artificial intelligence could alter the conditions under which financial institutions maintain cyber resilience. The paper was released on 2 November 2026 and formally presented at the Dubai FinTech Summit.
The paper, titled "Frontier and agentic AI: cyber resilience in the financial sector", centres its analysis on the deployed system rather than the underlying model. That framing is deliberate: the authors argue that what matters for resilience is what an AI system can access, the authority it holds, and the critical operations it can affect, not simply which foundation model sits beneath it.
Four dimensions of AI-related cyber resilience
The framework assesses cyber resilience across four connected dimensions: speed, reach, authority and trust. Speed concerns whether institutions can reduce material cyber exposure before it produces serious consequences, given that AI-enabled attack and defence activities can operate far faster than human incident-response cycles. Reach concerns whether institutions fully understand the shared technology, cloud infrastructure, identity services and software components they depend on, including those beyond their direct supplier relationships. Authority concerns whether consequential actions taken by agentic systems remain within their intended mandates. Trust concerns whether institutions can reconstruct what happened after an incident, bring unfinished activity under control, and reliably restore critical operations.
The paper argues that established frameworks are not obsolete, but that familiar evidence of compliance may no longer be sufficient to demonstrate their effective application. A patching deadline does not confirm that exposure has been reduced. A diverse supplier register does not confirm that fallback arrangements would withstand a relevant failure. Restored system availability does not confirm that unfinished transactions and financial records have been reconciled.
Mark Steward, Chief Executive of the DFSA, said the paper was intended to prompt "wider discussion on how regulators and firms can prepare for these developments", noting that the practical question for the authority is how agentic capabilities interact with access controls, delegated authority, critical financial operations and increasingly complex provider networks.
Regulatory and competitive context
The paper arrives at a moment when multiple regulatory bodies are grappling with how to adapt existing operational resilience and third-party risk frameworks to AI-augmented environments. In the UK, the Financial Conduct Authority and Prudential Regulation Authority are midway through implementing their own operational resilience rules, which require firms to map important business services and set impact tolerances. The EU's Digital Operational Resilience Act came into full effect in January 2025, imposing prescriptive requirements on ICT third-party risk management across EU-regulated financial entities. Neither framework was drafted with agentic AI in mind.
The DFSA operates within the Dubai International Financial Centre, a common-law jurisdiction that has positioned itself as a regulatory sandbox for emerging financial technology. Publishing a conceptual framework in advance of binding rulemaking is consistent with the DFSA's approach of consulting industry before legislating; it also gives the authority a vehicle for shaping international norms before larger jurisdictions codify their own standards.
Bryan Zhang, Co-Creator of C:\>DIR and Executive Chair of Fii, said the paper aims to offer "a common vocabulary for public sectors and private sectors working on them together", reflecting a view that no single firm, regulator or jurisdiction can settle these questions alone.
For enterprise security teams, the four-dimension taxonomy offers a practical audit lens: vendors marketing AI-powered security operations tools will increasingly need to demonstrate performance against speed and reach criteria, while governance functions will face harder questions about how to bound the authority of agentic processes operating across trading, settlement and identity systems. The paper does not propose binding rules or specific technical controls, but its framing is likely to inform future supervisory guidance from the DFSA and to be cited in peer regulatory consultations.